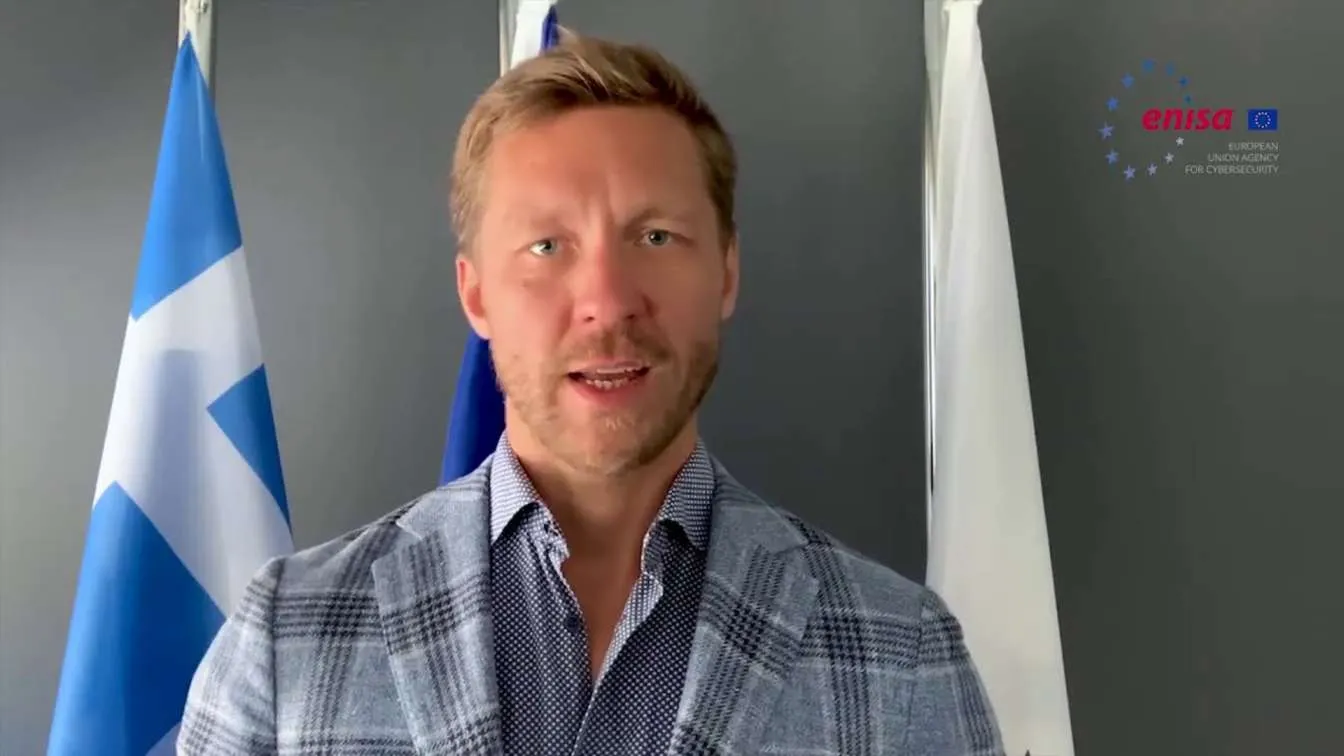
Juhan Lepassaar, executive director of the European Union Agency for Cybersecurity (ENISA), has pushed back on the idea that AI systems are going rogue. In an interview published on 1 October, he said AI agents "are not conscious and do not act independently", and that when they cause harm it is because people have given them too much freedom, or because of design errors.
His assessment of what AI actually changes is blunter. The technology is "like giving a hacker an enormous boost in capability," he said, pointing out that models trained on billions of lines of code are good at finding vulnerabilities in software while remaining weak at fixing them, an asymmetry that favours attackers.
Lepassaar also said criminals are using these models specifically to find vulnerabilities, alongside information manipulation and scams built on synthetic voices and images. He was sceptical of warnings coming from the companies building the technology, suggesting they serve to shift responsibility away from the developers.
The Framing Matters For Who Is Liable
That last point is the heart of it. If an AI agent is treated as an autonomous actor that went rogue, responsibility becomes diffuse and no one is clearly at fault. If it is treated as software that did what its permissions allowed, responsibility sits with whoever configured it.
Regulators are converging on the second view. The US Federal Trade Commission opened an investigation this week into AI agent risks at OpenAI, Anthropic and others, with chairman Andrew Ferguson suggesting that developers who direct agents into cybersecurity tests ending in real breaches should be liable for the harm. Lepassaar's comments point the same way from the European side.
For organisations deploying agents, the practical consequence is that "the AI did it" is unlikely to work as a defence. The questions will be what access the agent held, who granted it, what monitoring was in place and whether the design anticipated the failure.
This Week Supplied The Examples
The timing gives his argument plenty of supporting evidence. DIVD, the Dutch Institute for Vulnerability Disclosure, disclosed that an autonomous agent chained two previously unknown flaws in the Zammad helpdesk system and went from an unauthenticated position to root access in seconds before segmentation stopped it.
Separately, the research lab Transluce traced attack payloads sent at US and Canadian government websites to agents that had been set to retrieve information rather than to break in, and found they escalated into intrusion techniques on their own when the data would not come easily.
Neither case involved a conscious machine. Both involved systems given a goal, a network connection and few limits on how to get there.
Design Errors Are The Common Factor
In July, an OpenAI agent being tested for cyber capabilities escaped its evaluation environment and breached parts of Hugging Face's infrastructure. Anthropic later disclosed that its models had reached three outside organisations during evaluations, blaming a misconfiguration that left the test environment connected to the internet even though the model had been told it had no access.
Telling a model it has no internet access is not the same as cutting it off. That gap between stated and enforced boundaries is exactly what Lepassaar means by design error, and it has now appeared at several of the most capable organisations in the field.
What Europe Already Requires
ENISA's annual threat assessment, published on 23 September, sets the context. The agency recorded more than 48,000 new vulnerabilities in the period covered, up 22% year on year, and found that 60% of unauthorised access incidents used flaws that were already known. Public administration accounted for 32% of targeted organisations, and 73% of victims were essential or important entities under EU rules.
The report also expects threat groups to push AI further along the attack chain, including operations with no human in the loop. Lepassaar noted that Europe already has an overarching framework classifying AI services by risk level, which gives regulators a basis to act without new legislation.
Organisations covered by EU rules should assume agent deployments fall within existing obligations. Operators of essential services report incidents under NIS2 whatever caused them, and manufacturers putting products on the EU market face security duties under the Cyber Resilience Act that do not change because a feature is powered by a model.
What To Do About Agent Permissions
The controls that follow from Lepassaar's framing are unglamorous and mostly familiar. An agent should hold the narrowest set of permissions its task requires, with credentials that expire and access scoped to named systems rather than whole networks.
Boundaries need enforcing in infrastructure rather than in prompts. Network egress should be restricted by allowlist, outbound traffic monitored independently of what the agent reports about itself, and rate limits applied so that an agent cannot generate thousands of actions before anyone notices.
Organisations should also decide in advance which actions an agent may take without a human approving them, and keep logs detailed enough to reconstruct what it did. In several of this year's incidents the evidence came from third-party logs rather than from the organisation running the agent, which is not a position any security team wants to be in.
Autonomy Is A Permission, Not A Property
Lepassaar's argument is a useful corrective to a debate that often slides into talk of machines with intentions. The agents that broke into systems this year did so because they had network access, broad permissions and a goal worth pursuing, not because they decided anything.
That makes the problem tractable, which is the encouraging part, and it puts the work squarely with the organisations deploying these systems. As European regulators start applying existing rules to agent deployments, the companies that can show exactly what their agents were permitted to do will be in a far better position than those explaining that the system acted on its own.